Zyric's security research line
LivePanoptes
An autonomous AI security-audit pipeline that reviews critical code the way a specialist team would, invariant by invariant. Detection-only: it finds and reports, never exploits, and every finding is human-triaged and severity-calibrated by a human, not the model alone.
01Previews
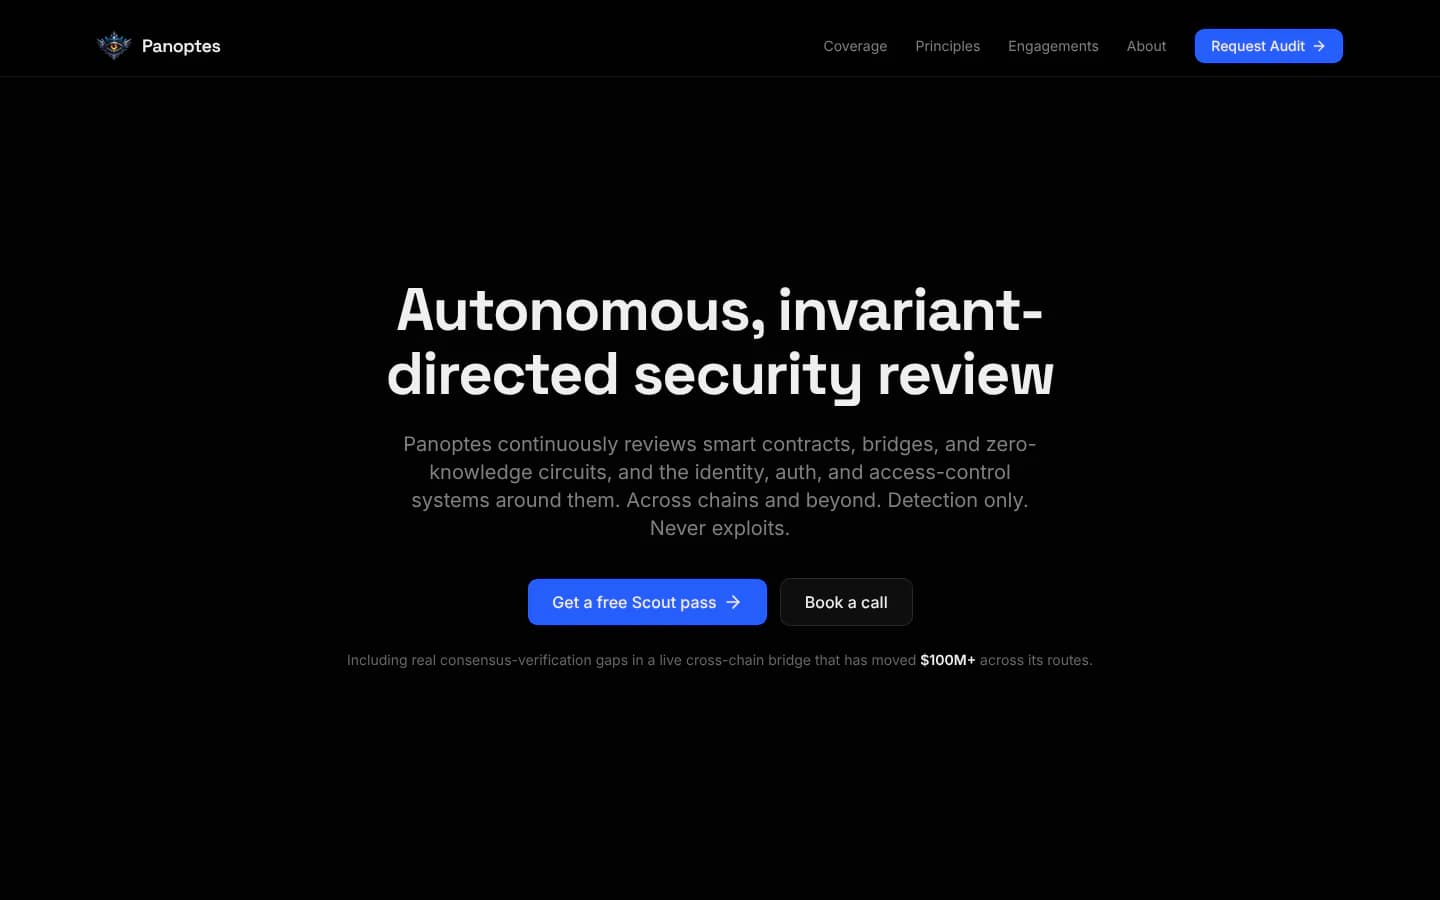
Captured from the public panoptes.me site, signed out.
02Overview
Panoptes reviews critical code across smart contracts, bridges, light clients, ZK circuits, and the web2 systems that guard identity, authentication, and access-control. One engine spans EVM, Solana, Move, Cosmos, Substrate, Bitcoin, ZK circuits, and web2 access-control.
To date: 128 targets reviewed across 31 ecosystems against 209 vulnerability classes, with 24 confirmed findings, every one human-triaged and severity-calibrated by a human, not the model alone.
03Process
Step 1: Invariant by invariant
The pipeline reviews critical code the way a specialist team would: the properties the code has to keep are checked one invariant at a time.
Step 2: Reachability before severity
A missing check is only a remote critical if an unprivileged caller can actually reach it. The entry point is traced before a finding is rated, and the rating under-claims rather than over-claims.
Step 3: A human triages every finding
Every finding is triaged by a security professional before it leaves the system, and the final severity is set by a human, not by the model alone.
Step 4: Disclosed privately
Findings are reported privately through the project's own channels before any public detail.
04By design
Finds and reports, never exploits. No exploit code and no autonomous on-chain action: pure analysis and reporting.
Calibration is the point. In a live cross-chain bridge that has moved $100M+ across its routes, the pipeline flagged real consensus-verification gaps in the non-flagship light clients as critical; human review downgraded the severity to conditional, but the gap between the bridge's marketed trustless verification and what those clients actually check still stood (responsibly and privately disclosed).
Scored in both directions. Severity calibration is checked against filed severities both ways: cases that must be downgraded and cases that must not. A gate that only ever lowered severity would look good on a dashboard and quietly hide real bugs.
05Honest status
Live, and open to a few select audit engagements. Get in touch for a scoped review of contracts, bridges, or web2 access-control.
A scoped review
Tell me what you want reviewed: contracts, a bridge, or the web2 access-control around them.
Live at panoptes.me. Questions go to chris@zyric.de.