A Zyric product
In DevelopmentFoundation
One control plane for the software a company runs. Foundation orchestrates the tools that already work, keeps every resource converging toward what you declared, and understands the repositories it runs, with humans and AI agents going through the same audited API.
01Previews
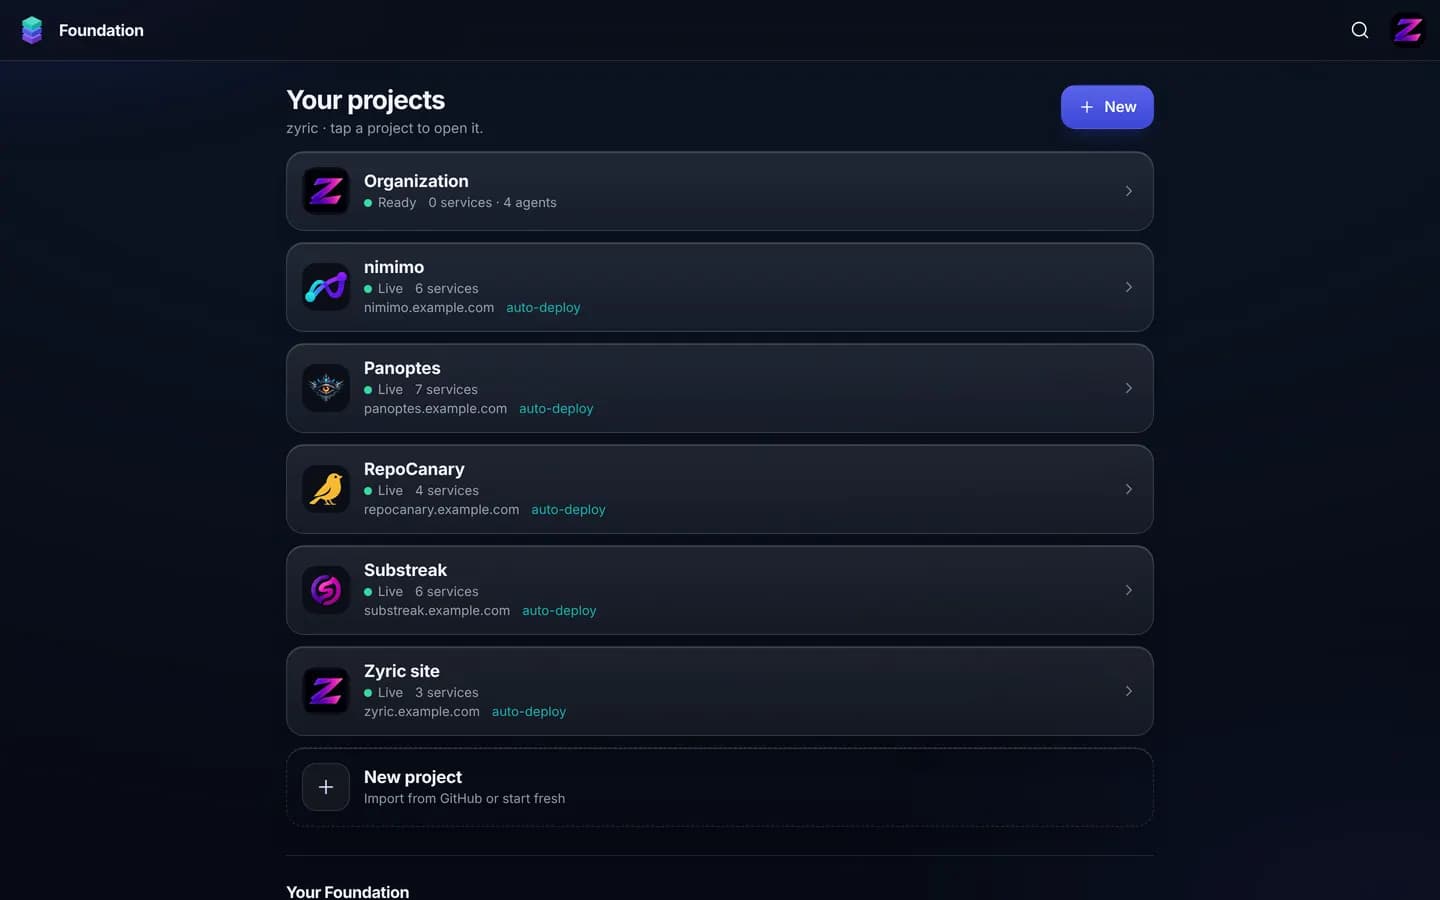
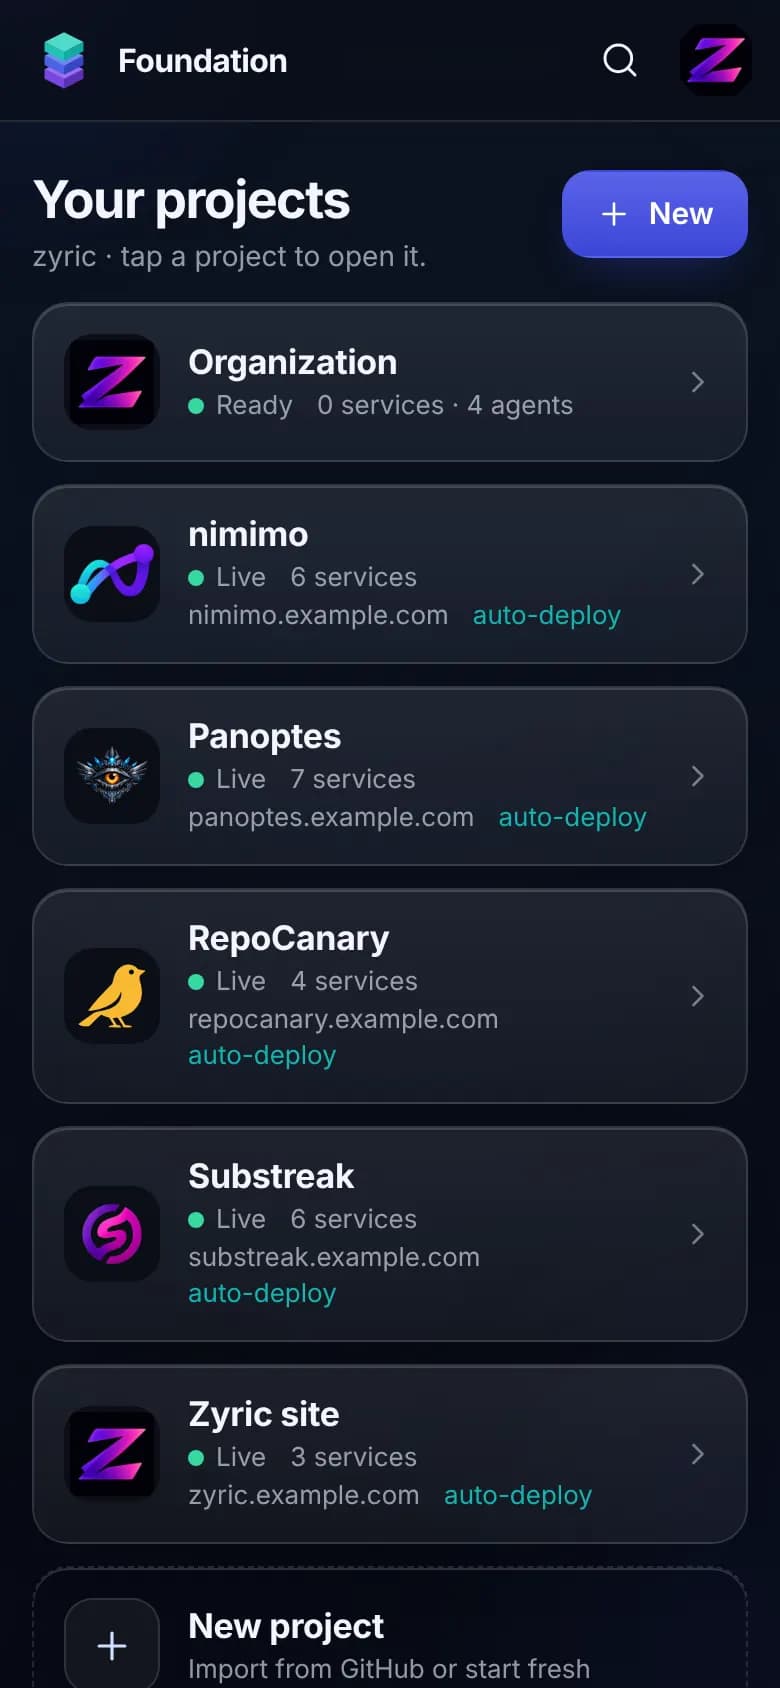
The real Foundation portal, rendered with demo data.
02Overview
Foundation is a single control plane and source of truth for everything a software company runs: projects, repositories, services, databases, secrets and domains. It does not replace the software you already trust. Docker stays Docker, Postgres stays Postgres; Foundation orchestrates them so they behave like one system.
Code names capabilities, such as a SQL database or a key-value store, never vendors, so the same declaration can run on a local container or a managed provider.
03Process
Step 1: Typed resources
Every project, repo, service and database is a typed resource with an identifier, a desired spec, an observed status and typed edges to the resources it depends on.
Step 2: Level-triggered reconciliation
Controllers converge what is running toward what was declared, on a durable queue. You change desired state, never click through a console, and every change has a history you can diff and restore.
Step 3: Repository Intelligence
Deterministic static analysis first: languages, endpoints, integrations and a basic security check, computed as facts. AI reviewers work on top of those facts rather than guessing from raw code.
Step 4: An MCP server
Any MCP client can inspect and drive the stack through the same API the portal uses, so an AI assistant gets real tools instead of screen scraping.
04By design
One audited API. Every actor, human or AI, goes through the one authorized, audited API. Access keys are role-scoped and can never exceed the scope they were minted with.
No privileged agent path. Agents have no side door. They call the same endpoints, under the same authorization and the same audit trail, as a person in the portal.
Envelope-encrypted secrets. Secrets are envelope-encrypted and never stored in the resource graph.
05Honest status
In active development, running in production on my own infrastructure, including this site. It is built and run under Zyric by one person, so early access is by request and hands-on.
Early access
Tell me what you run today and I will tell you honestly whether Foundation fits.
Or write directly to chris@zyric.de.